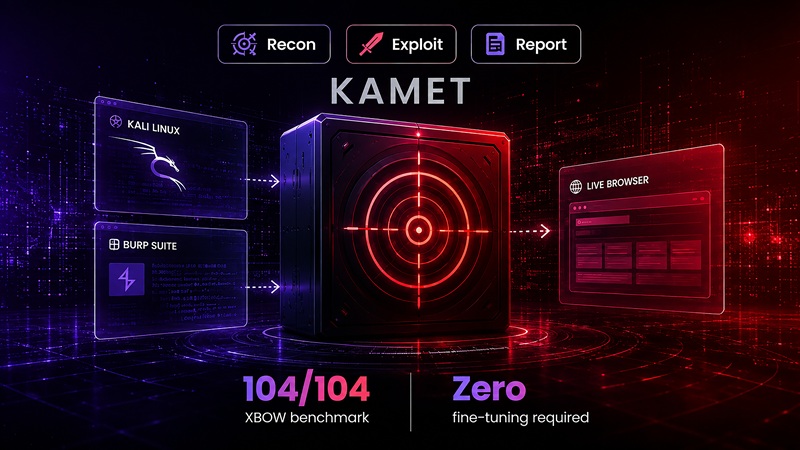
Our introduction, What Is AI Pen-Testing? Inside Kamet, covered the core idea: Kamet is an agent that drives a real Kali Linux attack box rather than a scanner with a summary attached. This post opens up what that attack box actually contains and how an engagement moves through it.
The workspace itself
Kamet runs from an agentic workspace console, the same kind of interface a human operator would use, except the operator issuing commands is the agent. Underneath it sits a live Kali Linux integration, so every tool the agent reaches for is the real thing, not an emulation of what that tool would output.
Mapping identity, not just scanning ports
A meaningful share of real-world breaches don’t come from an unpatched service. They come from an attacker abusing legitimate Active Directory relationships: a service account with too much delegation, a group membership that quietly grants domain admin three hops away. Kamet integrates with BloodHound to map those attack paths directly, which means the agent isn’t only asking what’s exploitable on a host, it’s asking what identity relationships actually lead to impact across the domain.
Web application testing, done through the same tools a human uses
Web application assessments run through a live web proxy integration, functionally the same role Burp Suite plays in a manual engagement: intercepting, inspecting, and manipulating requests as the agent works through an application’s logic rather than only fuzzing it from the outside.
Getting in, and staying connected
Two pieces handle the operational side of an engagement. VPN integration lets the agent manage its own connectivity into the engagement network, so it can reach in-scope infrastructure without a human establishing and monitoring the tunnel. Reverse shell integration handles the follow-through once a foothold is achieved, the step where a scanner’s job ends and a real penetration test’s job continues.
Mobile, without a separate toolchain
Mobile application security often becomes its own specialized workstream because static analysis of an APK or IPA needs its own tools and expertise. Kamet folds this in directly: a drag-and-drop interface accepts an APK or IPA file, and the agent runs static application security testing (SAST) against it using the same workspace and reasoning loop it applies everywhere else.
What the agent draws on
Across all of this, Kamet’s tool library spans 118+ tools and capabilities, organized as an agentic security skill library the agent selects from as an engagement develops, covering network, web, mobile, and the deeper technical disciplines like reverse engineering and binary exploitation described in our earlier post. If a specific capability isn’t already installed, the agent installs it rather than stalling the engagement.
From finding to chained path, with evidence
The difference this produces shows up at the end of an engagement, not just during it. Kamet’s attack-path view, similar in spirit to what BloodHound produces for Active Directory but applied across the whole engagement, shows how individual findings connect into a real path to impact, with a preview available once an engagement completes, so a client sees the chain that was actually walked, not a list of unrelated CVEs.
Where Kamet sits against the market
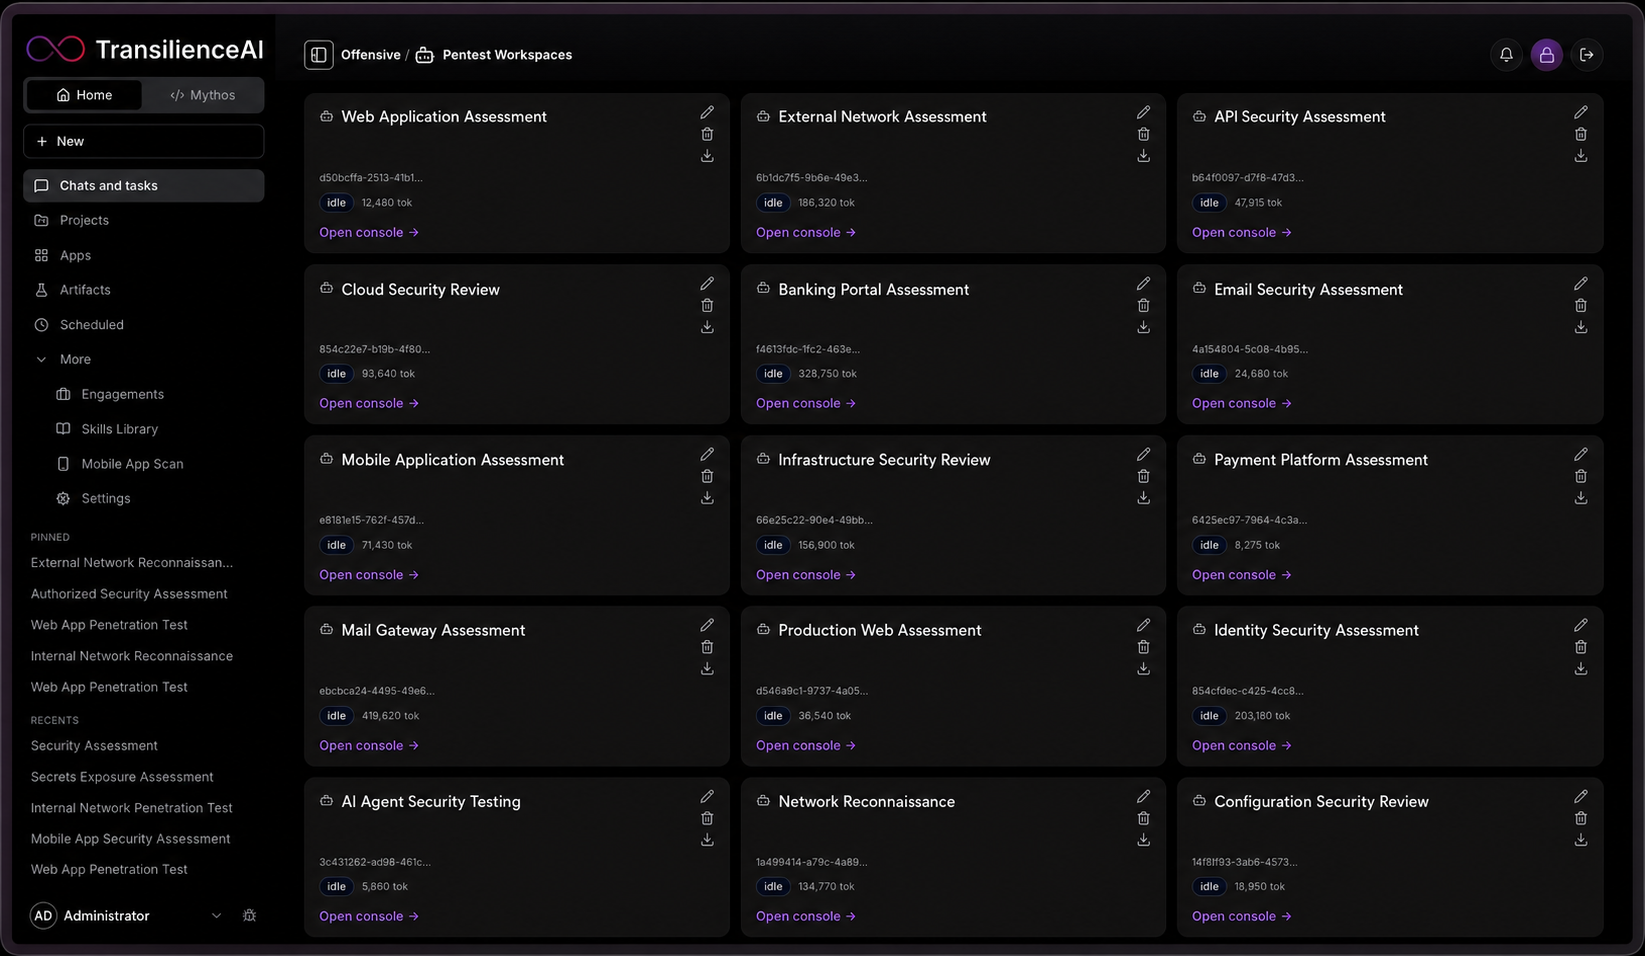
Most products marketed as “AI pentesting” fall into one of two categories: SaaS scanners that emulate known attack patterns against a fixed scope, or validation engines that confirm exposure without executing a full chained exploit. Kamet is built differently: a real attack box, with BloodHound, a live proxy, browser automation, and mobile SAST in the loop, running subagent parallelism to work multiple angles of an engagement at once. Vendors report where to look. This approach reports what actually got exploited, and how, the way an adversary would find it.
Safety still governs the agent
None of this removes the human from the loop where it matters. Commands flagged as dangerous still require explicit consent before execution, even in auto-run mode, a design choice that holds regardless of how much of the toolchain the agent is driving directly.
Who this is for
- Security teams evaluating “AI pentest” vendors who need to understand the difference between a scanner reporting exposure and an agent that drives BloodHound, a proxy, and exploitation tools together.
- Application security teams who want mobile SAST folded into the same engagement instead of a separate specialist workstream.
- Red teams and internal offensive security functions looking for a workbench that manages VPN connectivity, reverse shells, and tool selection without manual handoffs between stages.
- MSSPs delivering VAPT at volume who need attack-path evidence a client can actually read, not a raw findings export.
Curious what a chained attack path looks like in your environment? Book a Kamet walkthrough.