Continuous vs Annual Penetration Testing: What Changes With AI
For most organizations, penetration testing follows a familiar calendar. A test is scoped in the spring, executed over a couple […]
For most organizations, penetration testing follows a familiar calendar. A test is scoped in the spring, executed over a couple […]
Almost every organization runs some form of phishing simulation. Far fewer can say whether it has made them safer. The […]
Most security teams already have more findings than they can fix. Every scanner, every pentest, every cloud posture tool adds […]
Ask anyone who has run a third-party risk program what the job actually feels like, and the answer is rarely […]
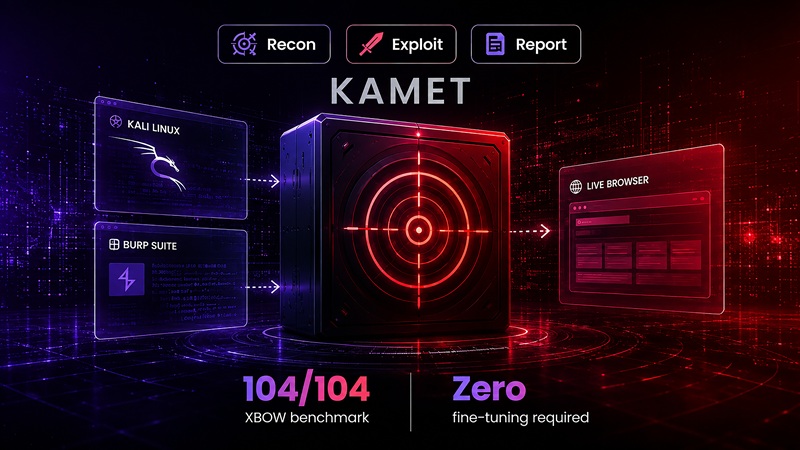
Most tools sold as “AI pentesting” today are automated scanners with a chatbot layered on top. They crawl a target, […]
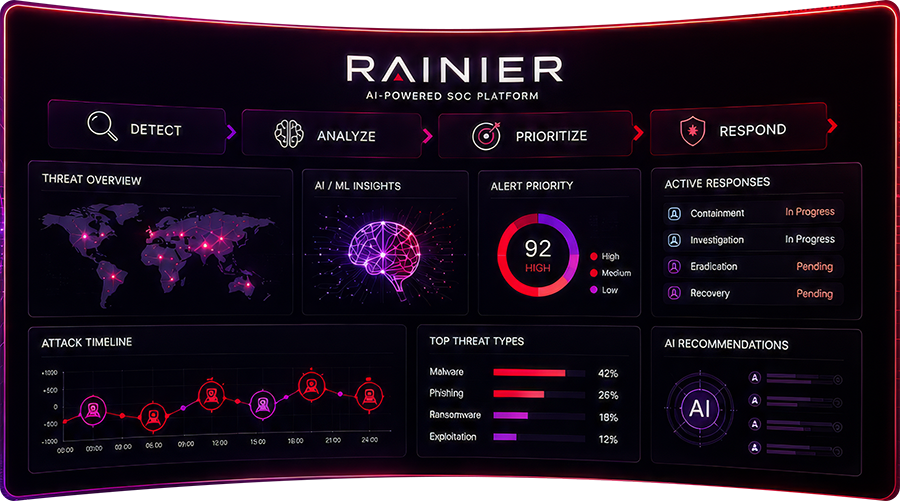
Ask most SOC teams what’s actually hard about their job, and the answer usually isn’t detection. Modern SIEMs and EDR […]
Most organizations seeking to meet SOC 2 requirements already know the framework exists. The challenge is understanding how the controls […]
Compliance, whether SOC 2 or otherwise, MUST be a continuous exercise. The absence of, or little attention to, it is […]

SOC 1 and SOC 2 are often mentioned together, but they serve very different purposes. The confusion usually starts when […]
A $400K annual contract, six months of sales effort, and three executive presentations. Then the procurement team sends a two-line […]